
Sebaraya Tech – A text says your package is on hold, or your bank account is locked, and there’s a link to fix it. Before you tap, you can usually spot a phishing link by checking three things: who sent it, what it’s pushing you to do, and where the link really goes.
Phishing messages are built to look official, so falling for one says nothing about how careful you are. This guide uses advice from the US Federal Trade Commission (FTC) and Google to show what to check, and what to do if you already clicked.
The Lures Phishing Messages Use
The FTC lists the stories scammers use most: suspicious login attempts, a problem with your account or payment, a request to confirm personal details, an invoice you don’t recognize, a refund you’re supposedly owed, or a free coupon.
They often open with a generic greeting instead of your name. And they push urgency, because a rushed reader skips the checks.
One rule cuts through most of it: legitimate companies won’t email or text you a link to update your payment information, according to the FTC.
Check the Sender First
In email, compare the sender’s display name with the actual address. Google advises checking that they match, since a message can show “Bank Support” as the name while coming from a random address.
Text messages are harder, because a short code or unknown number tells you little. Treat any unexpected text with a link as unverified until you confirm it another way.
For example, say a message claims to be from your bank. Close it, open your banking app or type the bank’s website yourself, and check for alerts there.
Read the Real Address Behind a Link
On a computer, hover your mouse over a link without clicking. If the address that appears doesn’t match where the link claims to go, Google says it may lead to a phishing site.
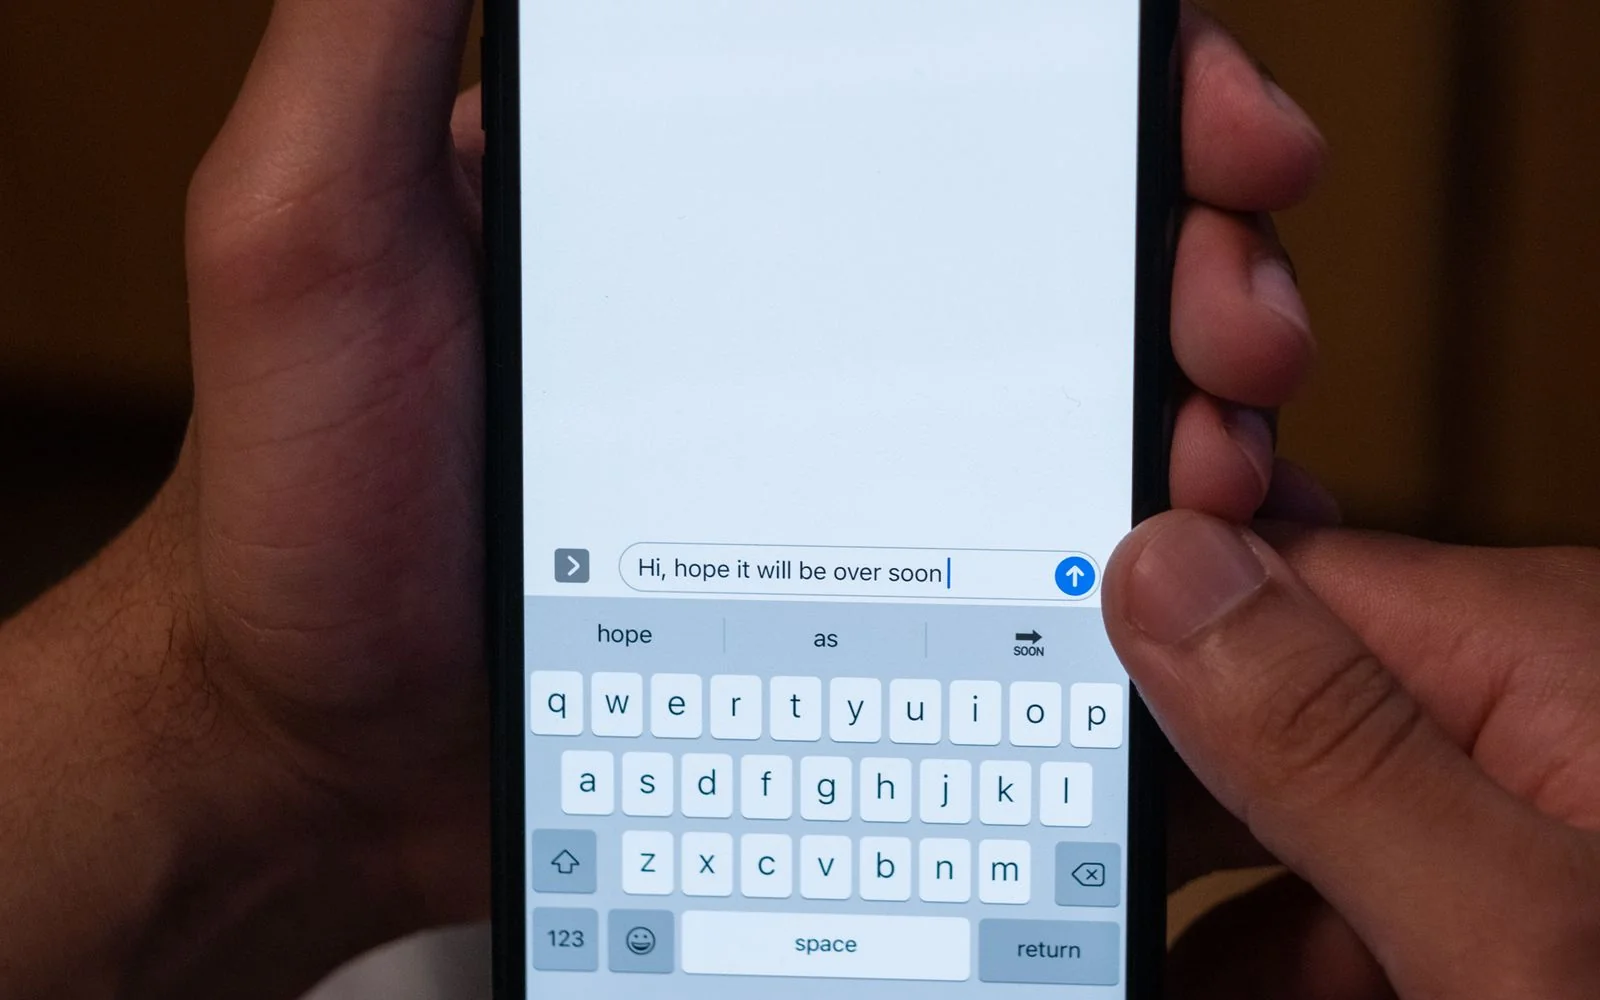
On a phone, pressing and holding a link (instead of tapping it) shows a preview of the address on many phones. Read it before opening anything.
How to Read a Web Address
The part that matters is the domain just before the first single slash. In an address like “yourbank.com.account-check.net/login”, the site actually belongs to account-check.net, not yourbank.com.
Watch for small swaps too: extra words, numbers replacing letters, or a different ending after the dot. If anything looks off, don’t open it.
When Gmail Warns You
Gmail sometimes shows a warning banner on suspicious messages. If you see one, Google advises not clicking links, downloading attachments, or entering personal information.
Google also notes that Gmail never asks for your password by email. Any message that does is fake by definition.
To flag a phishing email in Gmail on a computer, open it, click More next to Reply, and choose Report phishing.
If You Already Clicked
If you typed a password into a suspicious page, change that password right away on the real site, and on any other account that uses the same one. Turning on multi-factor authentication makes it harder for scammers to log in even if they have your password.
If you think the link installed something, update your security software and run a full scan. If you shared card or bank details, call your bank using the number on your card, not one from the message.
In the US, the FTC points victims to IdentityTheft.gov for step-by-step recovery. Outside the US, contact your bank and your country’s cybercrime or consumer protection agency.
Report It to Protect Others
The FTC suggests forwarding phishing emails to the Anti-Phishing Working Group at reportphishing@apwg.org, and phishing texts to 7726 (SPAM) on US carriers. US residents can also report at ReportFraud.ftc.gov.
After reporting, delete the message. Keeping it around only risks a mistaken tap later.
Next time a message rushes you, take that as the signal to slow down. Urgency is the scammer’s tool, not yours.
Komentar Ditutup! Anda tidak dapat mengirimkan komentar pada artikel ini.